The budget round is running and IT turns up with a list of a dozen or so line items. Most of them are renewals. Management asks which part of that is security, and nobody can answer without walking the list line by line. That is where a security budget in an SME fails first: not on the amount, but on the fact that nobody can say what the money is doing.
That is more uncomfortable than it sounds. A sum nobody can justify gets cut in every savings round and raised after every incident in the industry. Neither has much to do with the risk.
A security budget in an SME is rarely too small. It is usually invisible, spread across IT line items nobody labels as security. Sort the spend into three pots, operations, evidence and change, and you can justify for the first time what stays, what goes and what is missing. The number comes at the end of that work, not at the start.
Why the percentage question does not help
The question almost always comes first: what percentage of the IT budget is normal? Rules of thumb circulate, and they sound reassuring because they turn a decision into a calculation. The rule of thumb has two holes.
The first: the IT budget is not a neutral yardstick, it is the result of old decisions. A company that bought expensive infrastructure six years ago has a large IT budget and is therefore granted a large security budget on paper, without the risk having grown or shrunk. A percentage of a skewed base gives you a skewed number.
The second: two companies of the same size carry completely different exposure. A supplier with three large European customers gets security requirements delivered through the contract, whether it wants them or not. A 60-person fiduciary office has no supply chain issue, but it holds client data whose loss ends the business. The same percentage produces the wrong sum in both cases, once too high, once too low.
Most SMEs do not have a security budget that is too small. They have one that is invisible. In our experience, more protection regularly comes from line items disappearing rather than from new ones arriving.
How much security budget does an SME need?
As much as running what you already have costs, plus the risks you deliberately do not want to carry. The order matters more here than the sum. In most SMEs the larger share of the money is already in the house, just not under the label of security. Make visible first what is already running, and the additional figure you then discuss is much smaller.
Part of that spend is not negotiable, whatever last quarter's margin looked like. A backup that gets restored regularly. Identities that actually expire when someone leaves. Systems that get patched. Logs that someone reads. That is operations, comparable to the heating: dull, continuous, and nobody celebrates it. The negotiable part starts above that. It depends on what a standstill costs you and who has a contractual right to look over your shoulder. Headcount says little about it.
One line item is missing from almost every one of these budgets: the leadership itself. Somebody has to decide what does not get bought, and defend that decision to management, the board and customers. We broke down what that role costs in Switzerland in the honest calculation on CISO cost. Without that item, the budget stays a shopping list.
The three pots security money sits in
Once the spend is on the table, it sorts itself almost by itself into three groups. The split is not a bookkeeping exercise, it changes who decides what.
- Operations. Licences, managed services, backup, monitoring, patch management. Predictable, recurring, usually the largest pot. Discussions here are efficiency discussions, not risk discussions.
- Evidence. Audits, certification, customer questionnaires, penetration tests a customer asks for. Driven by sales and by regulation, not by the threat picture. This pot grows with your customer list.
- Change. Time-boxed work: multi-factor authentication across the board, network segmentation, building an ISMS. It ends when it is done, and then partly moves into operations.
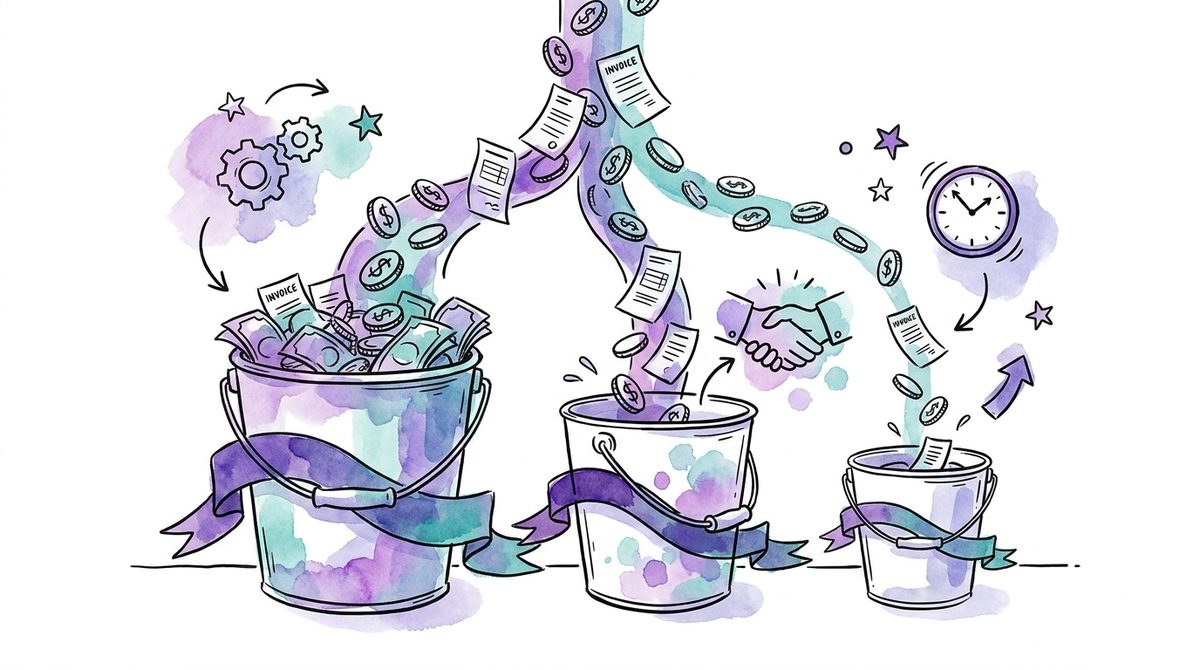
The value of the split shows up in the meeting. Put everything into one sum and every discussion turns political: every cut sounds like negligence, every increase like panic. Split apart, it becomes visible that the operations pot is a cost question, the evidence pot a sales question, and only the third pot is genuinely up for discussion. It also becomes visible when a change project creates permanent operating costs nobody planned for. In our experience that is the most common reason budgets get tight in the second year.
What this looks like in a Swiss SME
In one mandate at an industrial company with a good 200 employees and two sites, management assumed a security budget in the low five figures. That was the sum of the line items booked under security in the system.
Taking stock surfaced three further sources. A security module was running inside the managed service contract with the IT provider, paid for years and never reviewed. Two subscriptions for vulnerability scanning covered the same job, bought by two people at different times. An awareness platform was billed per head, although a large part of the workforce had never opened it.
The real sum was well above the assumption. The consequence was still not a cut. We moved the money, away from the duplication and towards what the largest customer wanted to see in the audit. How that clean-up works in detail is covered in the post on consolidating security tools. For management the more important effect was a different one: for the first time there was a number somebody in the house could defend, because they knew what sat behind it.
Why a security budget fails in front of the board
A board cannot judge whether you need an endpoint product from vendor A or vendor B. It can and must judge which disruption the company can absorb. That translation is missing from most budget papers, which is why they get a yes with a furrowed brow or a no without a reason.
A paper that holds up answers three things in the language of the board: what happens to the business if this item is cut. Which obligation towards customers or a regulator hangs off it. And which risk the board accepts if it strikes the item. The last point is the uncomfortable one, and it is the only one that keeps budgets stable. An accepted risk is a decision with a name on it. A struck item without that decision is only a deferred invoice.
It also explains why security budgets jump after an incident at a competitor and collapse again twelve months later. Where no decision is on record, mood decides.
What does it cost not to decide the budget?
Nothing in the short term, and that is exactly the problem. The price arrives later, in three places. First in sales: if you cannot evidence in a customer questionnaire what you actually run, you lose weeks or the deal. Second in an incident, where everything gets bought at emergency rates, including the external help. Third in subscription sprawl, which quietly renews every year because cancelling would be a decision and nobody owns it.
Then there is the calendar. The Swiss ISG (Informationssicherheitsgesetz, the federal information security act) has obliged operators of critical infrastructure since 1 April 2025 to report cyberattacks within 24 hours to BACS, the federal cyber security office (BACS information on the reporting obligation). By 31 December 2026, organisations subject to the ISG need a functioning ISMS. Many SMEs are not directly in scope, but get the requirement written into the contract by their customers. Budget for it only in autumn 2026 and you pay for the same build under time pressure.
How to recognise a security budget that holds up
Four characteristics that have proven themselves in practice. None of them has anything to do with the amount.
- Every line item has a name next to it, not a department. Whoever owns it can explain what happens without it.
- Operations, evidence and change are shown separately, so a savings round does not land on the backup because it happened to sit at the top of the list.
- There is a list of what was declined. A budget without items that are deliberately not funded is not a prioritisation, it is a wish list.
- The unfunded points are recorded as accepted risk, with a date and the body that accepted them. That is the part auditors and insurers want to see first.
With those four points you do not need a benchmark any more. The number follows, and it survives the questioning in the board meeting. If nobody in the house has the time to do that sorting properly once, this is exactly the case senior security leadership on a mandate exists for: the three fixed-price packages usually start with taking stock, and the basis for the budget falls out of that anyway.
Frequently asked questions
Does the security budget belong to IT or to management?
The spend usually runs through IT, the decision belongs with management. The reason lies in liability. IT can judge what something costs and what it achieves technically. Whether a residual risk is bearable is decided by whoever answers for the business. Bundle both inside IT and you get a budget nobody outside IT can defend.
Does cyber insurance count towards the security budget?
Yes, and it belongs in there visibly, because it shifts decisions. A policy replaces no control, it only changes who carries the cost of a loss. On top of that, insurers today ask for evidence on backup, multi-factor authentication and the ability to respond. Producing that evidence costs money, which belongs in the evidence pot and is missing from many budgets.
What if it becomes clear mid-year that the budget is not enough?
Then usually a new customer promise or a new obligation has arrived, not a new threat. That is good news, because a supplementary request can be justified with a specific customer or contract rather than with a feeling. It only gets difficult when nobody can say which of the existing items could give way for it.